

About integrations
Integrations connect Base44 to the rest of your stack so you can automate workflows, pull in data, and call external services without wiring every API call by hand. You can integrate at 3 levels:- App level: Integrations inside a single app:
- Built-in integrations such as Invoke LLM and SendEmail.
- Connectors for OAuth-based connections to tools like Notion, Slack, or Google Workspace.
- External API calls with backend functions that use per-app Secrets and functions.
- An app MCP server that lets AI assistants like Claude, ChatGPT, and Cursor securely connect to your published app and use its data and actions.
- Workspace level: Shared APIs managed once for the whole workspace:
- Custom OpenAPI integrations based on OpenAPI specs that any app in the workspace can call securely.
- Account level: Connections that live on your Base44 account:
- MCP connections that you configure once so the Base44 AI chat can use external tools while you build, without changing your app’s deployed code.
App level integrations
App-level integrations live inside a single app. They include built-in integrations, connectors, and backend-powered external APIs that you wire to that app only.Built-in integrations
Some integrations come preinstalled in Base44 and are available to use immediately. Most work on any plan, with no extra setup or separate API keys. With these core integrations, you can add AI, messaging, file handling, and advanced logic to any app. Base44 built-in integrations include:- Invoke LLM: Generate AI responses from the built-in language model using detailed prompts. Supports JSON schema outputs, file attachments for added context, image analysis, and web search for up-to-date information.
- SendEmail: Send emails from your app with customizable sender names and rich HTML content, or send one of your designed emails. Anyone who has signed up to your app can be emailed on any plan. To email an address that has not signed up, your app needs a paid plan and a verified custom domain.
SendEmail does not support sending to external mailing lists. It can attach up to 5 files, up to 5 MB each and 10 MB in total.
- SendPushNotification: Send a native push notification to one person in your app, with an optional link to a specific page.
SendPushNotification needs a native mobile app with push notifications set up.
- UploadFile: Let people upload files to your app. Use the returned file URL in other integrations or workflows.
- GenerateImage: Create images from detailed text prompts, on their own or from existing images you give it as a reference. Returns a URL to the generated image.
- ExtractDataFromUploadedFile: Pull structured data from uploaded files (CSV, PNG, JPG, JPEG, PDF) using JSON schemas. Useful for importing data in bulk.
Connectors
Connectors are OAuth-enabled integrations that let a specific app connect to supported tools. You ask the AI chat to connect a service, sign in, and approve the requested permissions. Your app can then read or write data in that tool based on what you allow. Examples of what you can build with connectors:- Sync a Notion database to power a knowledge view in your app.
- Post updates to a Slack channel.
- Sync Salesforce or HubSpot records into an internal dashboard.
- Save files from your app to Google Drive.
- Block off time in Google Calendar when a new booking is made.
- Publish a LinkedIn post when a new blog post is published.
- Show TikTok profile stats and follower counts in a dashboard.
External API calls with backend functions
External integrations using backend functions let a specific app talk directly to third-party services like Stripe, Twilio, or Google APIs with per-app credentials. These calls are wired through your own backend functions and Secrets.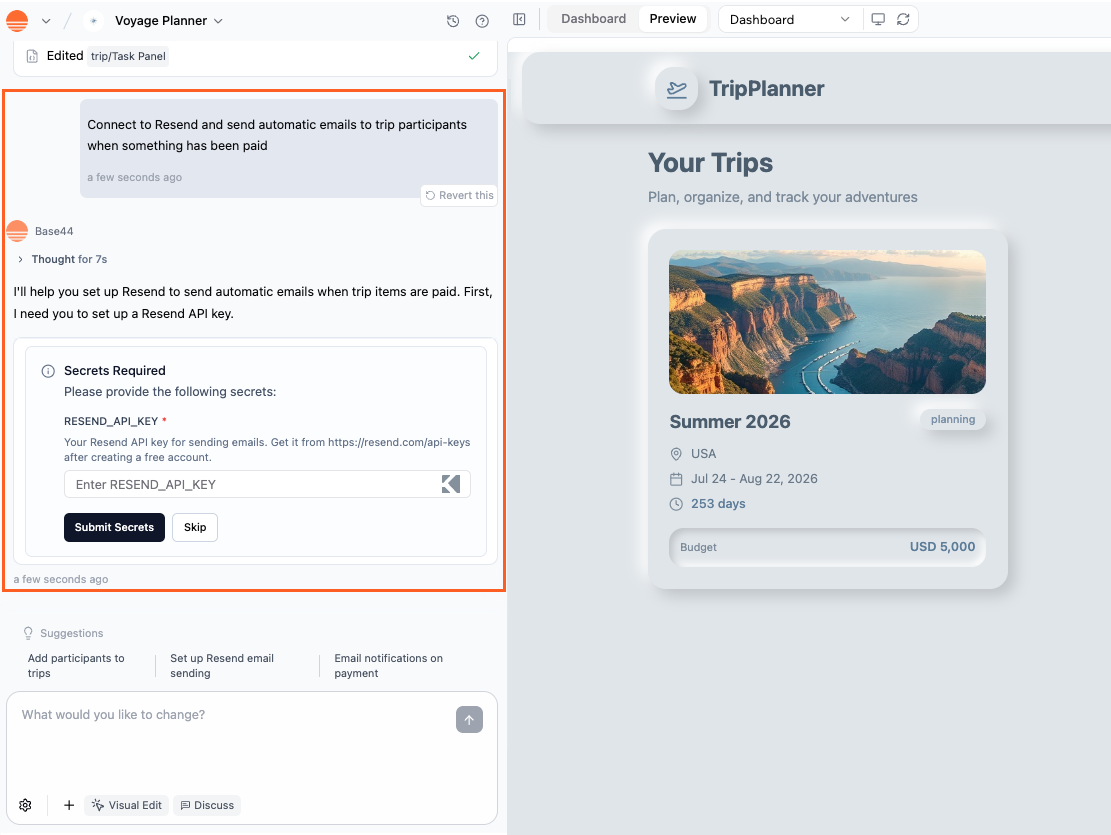
Connecting an integration to your Base44 app using the AI chat
- You want a one-off integration for a single app.
- You need custom logic that is tightly coupled to that app.
- The service is not yet set up as a custom OpenAPI integration in your workspace.
- Sending welcome emails to new people using your app via your email provider.
- Syncing your existing CRM with your app database.
- Alerting your team in Slack when someone submits a form.
- Generating content with AI tools using your own provider keys.
- Calling vendor-specific APIs that do not have a connector or custom OpenAPI integration yet.
base44 > functions. Learn how to add, change and delete your app’s secrets.
Connecting AI assistants
Your published app can expose its own MCP server so AI assistants can use its data and actions, with access controlled by you. This is different from account-level MCP connections, which the Base44 AI chat uses while you build.Workspace level integrations
Workspace-level integrations live in a workspace and can be reused across many apps without repeating setup or credentials.Custom OpenAPI integrations
Custom OpenAPI integrations let you register shared external APIs at the workspace level from an OpenAPI specification. You import a spec once, select the operations you want to expose, and any app in that workspace can call those operations through the SDK. The AI and your frontend code can call custom OpenAPI integrations directly throughbase44.integrations.custom without exposing credentials. Calls are proxied through the Base44 backend, so secrets never reach the browser.
This is ideal for internal APIs and partner APIs that your team uses across many apps.
Account level connections
Account-level connections are configured once for your Base44 account and are available wherever you use the Base44 AI chat.MCP connections
MCP connections let you connect custom MCP servers to your Base44 account so the AI chat can use external tools and data as context while you build. This gives you a context-aware AI chat without changing your app’s deployed runtime. Examples of what you can do with MCP connections:- Ask the AI chat to search an internal docs MCP and summarize the most relevant pages for a feature.
- Connect a GitHub MCP server and ask for a summary of open issues in a specific repo.
- Connect an analytics MCP, such as Amplitude or a custom metrics service, and ask the chat to pull recent product metrics into the conversation while you plan changes.
Getting your API keys
Some integrations require an API key, which acts like a private password between Base44 and the external service. Your API key proves ownership and keeps your connection secure. Base44 stores your key safely so your app can use it without exposing it. To get your API key:- Log into the external service (for example, OpenAI, Resend, Notion).
- Find the Developer, API, or Integrations section.
- Click Create API Key or Generate Token and copy it.
- Paste your API key in Base44:
- Using the AI chat: Enter your API key in the AI chat when prompted.

Pasting a key into the AI chat
- Setting up manually: Save your API key as a secret in your app’s dashboard. See Adding secrets.
- Using the AI chat: Enter your API key in the AI chat when prompted.
Managing app secrets
Secrets are where your app keeps API keys, tokens and passwords, so its backend functions can use them without the values ever showing up in your app’s code. You add, change and delete them from the Secrets page in your app’s dashboard.Adding secrets
Add a secret when a service gives you a key your app needs. If the AI chat asks you for a key, you can paste it there instead, and it’s saved as a secret for you. Your backend functions find each secret by its exact name. If the AI chat already wrote a function that expects a key, use the name it gave you. To add a secret:- Click Dashboard at the top of the app editor.
- Click Secrets.
- Click Add Secret.
- Enter the Secret Name, for example
STRIPE_API_KEY. Names can’t contain spaces, so use underscores. - Paste the key into Secret Value.
- Click Add Secret.
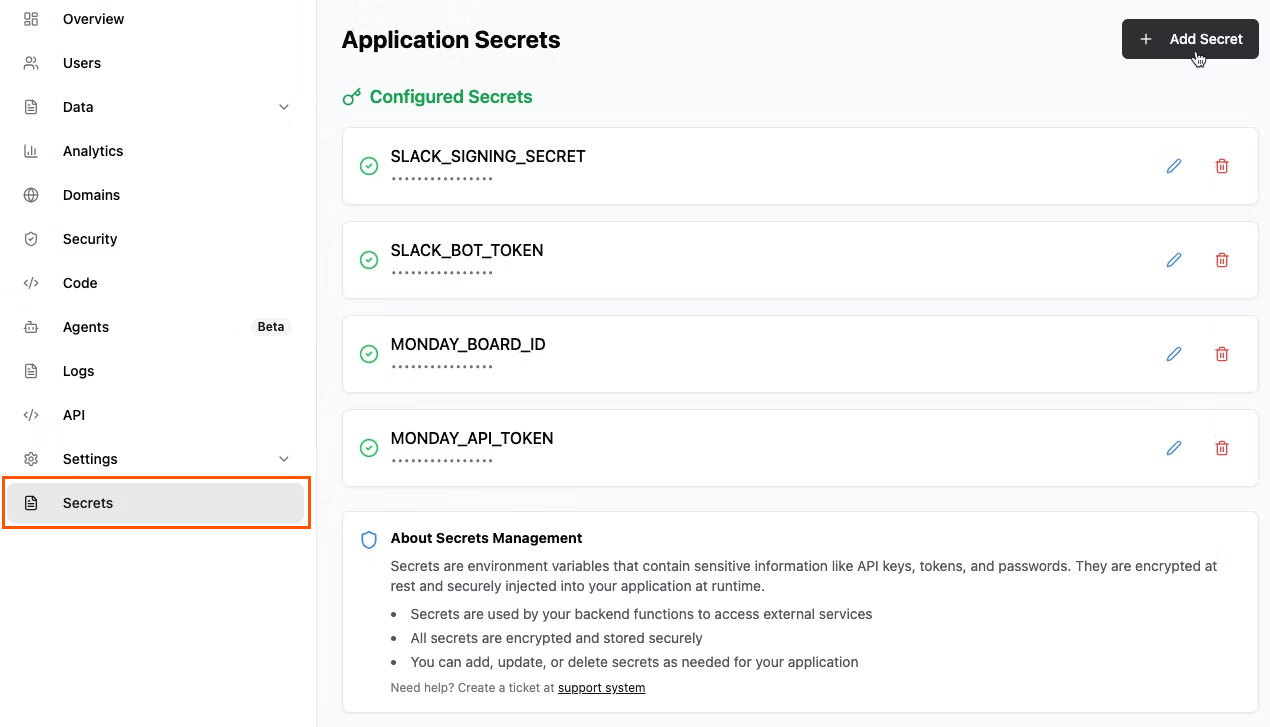
Your app's saved secrets
Changing or deleting secrets
Update a secret when you regenerate a key in the service it comes from, and delete it when your app no longer uses that service. Choose what you want to do:Change a secret's value
Change a secret's value
You can replace a secret’s value, but you can’t rename it. To use a different name, add a new secret and delete the old one.To change a secret’s value:
- Click Dashboard at the top of the app editor.
- Click Secrets.
- Click the edit icon next to the secret.
- Paste the new value.
- Click Save.
Delete a secret
Delete a secret
Deleting happens straight away, with no confirmation, and you can’t undo it. A function that still reads the secret gets no value, so ask the AI chat to remove or update that code too.To delete a secret:
- Click Dashboard at the top of the app editor.
- Click Secrets.
- Click the delete icon next to the secret.
Applying your changes
When you add, change or delete a secret, your backend functions pick up the change automatically while you build and preview. Your published app keeps the values it had when you last published, so publish your app again to make your live app use the change.Keeping secrets private
Secrets are encrypted and stored securely, and they stay on the server. Your backend functions read them when they run, so the full secret values never reach the browser or the people using your app. After you save a secret, its full value stays hidden, even from you. When you save a value of 30 characters or more, such as most API keys, the Secrets page shows its first 10 characters, so you can tell which key is saved. Shorter values stay fully masked. Anyone who can edit your app can see these hints and add, change, or delete its secrets. Keep your own copy of any key you can’t regenerate.FAQs
Click a question below to learn more about using integrations.What is the difference between custom OpenAPI integrations and per-app external APIs?
What is the difference between custom OpenAPI integrations and per-app external APIs?
Custom OpenAPI integrations are configured once in a workspace from an OpenAPI spec and are available to every app in that workspace through
base44.integrations.custom.call(). Credentials are stored as encrypted workspace secrets and never exposed to app code, and you do not need backend functions to use them.Per-app external APIs use backend functions and Secrets in a specific app. They are ideal for app-specific logic or when you do not want to share an API across all apps in a workspace.How should I test my integration before I publish?
How should I test my integration before I publish?
Before publishing your app, test your integration so you can catch issues early:
- Use sandbox or test mode (for example, Stripe test keys), if the provider offers it.
- Try real flows and edge cases, not just a single happy path.
- Check that inputs and outputs match your expectations in your UI and in the provider’s dashboard.
- Monitor integration credit usage in both Base44 and the external service.
- Preview your app to catch slow loading, failed API calls, or missing data before going live.
Why is my integration not working?
Why is my integration not working?
If you run into issues, check the following:
- Your workspace is on a Builder plan or higher (for per-app external APIs that use backend functions).
- Your API key is correct and saved in Secrets or in the custom OpenAPI integration, if relevant.
- You have enough active credits in the external service.
- You are using live credentials, not test ones, when testing production flows.
- Your API request includes the correct endpoint, payload, and parameters.
- You have not hit the service’s rate limits.
Who can use backend functions and per-app external APIs?
Who can use backend functions and per-app external APIs?
Backend functions and per-app external APIs require a Builder plan or higher on the workspace where the app was created. If the workspace is on a Free or Starter plan, backend functions and integrations that depend on them are unavailable.Workspace owners and admins can create backend functions in apps they own. Collaborators with an Editor role can also edit and create backend functions in an app as long as the workspace has a Builder plan or higher.
Why do I get 403 errors when using backend functions?
Why do I get 403 errors when using backend functions?
If you see a 403 error when using backend functions, it may mean backend functions are not available for your app or workspace, or the request is missing permissions.Common causes and fixes:
- Plan requirement: Backend functions are only available on a Builder plan or higher. If the workspace is on a Free or Starter plan, backend calls and per-app integrations that rely on them can fail with 403.
- Permissions in your function: Your backend function may be rejecting the request because the person is not signed in or does not have the right role. Check any role or access checks you added in the function code.
- External service permissions: A 403 can also come from the external API you are calling. Make sure the API key has the right scopes and that the request uses the correct endpoint and method.
- Still having trouble: See the backend function fixes in Base44 developer tools, or contact Customer Care.
How do I regenerate or update my API key?
How do I regenerate or update my API key?
There are 2 types of API keys you may need to regenerate or update:
- Third-party service keys: Regenerate your key in that service’s developer portal, for example OpenAI, Resend, Notion, then change the secret’s value in your app’s dashboard or update it in your custom OpenAPI integration settings.
- Your Base44 account API key: Account API keys are no longer supported, and you can’t regenerate one. Existing keys are being switched off gradually, so create a personal access token instead and update anything that used the old key.
What happens to my integrations if I downgrade my plan?
What happens to my integrations if I downgrade my plan?
- Built-in integrations remain available.
- Connectors, custom OpenAPI integrations, MCP connections, and per-app external APIs that rely on backend functions may stop working until you upgrade to a Builder plan or higher.
Can my app send text messages?
Can my app send text messages?
Base44 doesn’t send text messages (SMS) itself. To send them from your app, sign up with an SMS service, save its API key as a secret, and ask the AI chat to send messages through a backend function. For example:
Can I use multiple integrations in one app?
Can I use multiple integrations in one app?
Yes. You can mix built-in integrations, connectors, custom OpenAPI integrations, and per-app external APIs in the same app, as long as your plan and settings support them.
Why can Base44 or the AI not fetch my API key for me?
Why can Base44 or the AI not fetch my API key for me?
For security reasons, external services like Stripe, OpenAI, or Notion do not let third parties, including Base44, access your credentials automatically. Instead, you need to:
- Log in to the service.
- Go to the API or developer section.
- Generate your key.
- Paste it into Base44 as a Secret or workspace header.
Why this matters: API keys act like passwords for services. Keeping them private and under your control keeps your data safe and ensures only you authorize access.
Do MCP connections work like other app integrations?
Do MCP connections work like other app integrations?
No. MCP connections are only for the Base44 AI chat while you build. They are configured at the account level under Settings → MCP Connections and are used only when your prompt requires that MCP server. Your deployed app does not call MCP servers through this settings page.